Author profile
Rex Liu
Co-founder, General Analysis
39 works
Authored research and guides
 Guide·PLAYBOOK
Claude Managed Agents: Require approval for sensitive tools
Configure Claude Managed Agents tool approvals, separate customer intent from reviewer authority, and recover pending calls without blindly repeating actions.
September 13, 2026 · 7 min read
September 13, 20267 min read
 Guide·PLAYBOOK
Claude account restrictions: Close personal access and old connections
Deploy Claude tenant and connector restrictions, review existing OAuth grants, and verify which account and network paths your Enterprise rollout covers.
September 12, 2026 · 7 min read
September 12, 20267 min read
 Guide·PLAYBOOK
OpenAI Agents API: Manage self-hosted sandbox lifecycles
Connect an Agents API self-hosted sandbox, handle reconnects and uncertain tool outcomes, and clean up session state and provider compute without leaving orphaned work.
September 11, 2026 · 7 min read
September 11, 20267 min read
 Guide·PLAYBOOK
GitHub Copilot managed permissions: Deploy and verify policy
Deploy GitHub Copilot managed permissions, check which users receive them, resolve team and device policy conflicts, and verify approval behavior before rollout.
September 10, 2026 · 8 min read
September 10, 20268 min read
 Guide·PLAYBOOK
Microsoft 365 Copilot: Collect prompts and reconcile audit logs
Collect Microsoft 365 Copilot prompts and responses through Graph, reconcile them with Purview audit records, and track missing evidence without assuming full coverage.
September 9, 2026 · 8 min read
September 9, 20268 min read
 Guide·PLAYBOOK
Claude ant apply in CI: Preserve state when deployments fail
Use Claude ant apply in CI with reviewed plans, scoped workload identity, serialized updates, and a recovery procedure that preserves partial deployment state.
September 8, 2026 · 7 min read
September 8, 20267 min read
 Guide·FRAMEWORK
OWASP LLM Top 10 2026: From Rankings to Runtime Controls
A technical guide to the OWASP LLM Top 10 2026: its evidence-weighted ranking, model-versus-agent boundary, and the controls to verify before release.
September 4, 2026 · 10 min read
September 4, 202610 min read
 Guide·FRAMEWORK
OWASP Agent Control Standard (ACS): What It Controls and What It Doesn't
A technical guide to the OWASP Agent Control Standard: its Guardian boundary, v0.1 schemas, roadmap gaps, failure modes, and an implementation test plan.
September 2, 2026 · 8 min read
September 2, 20268 min read
 Guide·PLAYBOOK
Claude Code Enterprise Security Deployment
Enterprise deployment guide for Claude Code security across managed settings, identity, dev containers, proxy controls, MCP, hooks, OpenTelemetry, CI/CD, and governance.
May 22, 2026 · 24 min read
May 22, 202624 min read
 Guide·PLAYBOOK
Claude Code Control and Observability with OpenTelemetry
Set up Claude Code OpenTelemetry (OTel), lock the collector destination, audit tool and MCP events, and route production telemetry to a SIEM.
May 22, 2026 · 23 min read
May 22, 202623 min read
 Guide·PLAYBOOK
Claude Code Settings, Permissions, and Bash Tool Security
A practical guide to Claude Code settings, permission rules, Bash tool controls, hooks, MCP allowlists, telemetry, and safe defaults for developer teams.
May 21, 2026 · 21 min read
May 21, 202621 min read
 Guide·PLAYBOOK
Best Automated Penetration Testing Platforms in 2026
A practical 2026 buyer guide to automated penetration testing platforms, autonomous pentesting, automated security validation, CTEM, DAST, BAS, and AI security testing.
May 21, 2026 · 18 min read
May 21, 202618 min read
 Guide·PLAYBOOK
Best AI Security Platforms in 2026
Compare AI security platforms by discovery, agent controls, red teaming, runtime protection, and model security, with dated sources and practical buying questions.
May 21, 2026 · 6 min read
May 21, 20266 min read
 Guide·PLAYBOOK
Security Guidance for Claude Cowork and Risks
Claude Cowork can reach local files, browser sessions, plugins, MCP servers, scheduled tasks, connectors, and approved desktop apps. This guide explains the main Claude Cowork risks and the security controls enterprises should put in place before broad rollout.
May 20, 2026 · 13 min read
May 20, 202613 min read
 Guide·PLAYBOOK
Anthropic Claude Code Security Best Practices
Security best practices for Anthropic Claude Code across permissions, Bash, hooks, MCP, sandboxing, proxy controls, telemetry, and CI/CD workflows.
May 20, 2026 · 22 min read
May 20, 202622 min read
 Guide·PLAYBOOK
How to Secure Claude Code
A practical enterprise guide to securing Claude Code with permissions, sandboxed Bash, dev containers, managed settings, MCP allowlists, hooks, proxy controls, OpenTelemetry, and CI/CD release gates.
May 19, 2026 · 22 min read
May 19, 202622 min read
 Guide·PLAYBOOK
Best AI Red Teaming and Adversarial Testing Tools in 2026
Compare PyRIT, garak, Inspect, DeepTeam, and commercial AI red teaming tools by use case, evidence, and operating cost. Includes a free evaluation worksheet.
May 19, 2026 · 9 min read
May 19, 20269 min read
 Guide·PLAYBOOK
How to Secure Coding Agents
A concise summary of the General Analysis technical whitepaper on securing Claude Code, OpenAI Codex, Cursor, Windsurf, Devin, GitHub Copilot, and Claude Cowork.
May 11, 2026 · 6 min read
May 11, 20266 min read
 Guide·PLAYBOOK
How to Detect Shadow AI
A practical guide to detecting shadow AI across browser extensions, SWG endpoint agents, network telemetry, SaaS logs, endpoint agents, AI gateways, and MCP gateways.
May 7, 2026 · 13 min read
May 7, 202613 min read
 Guide·PRIMER
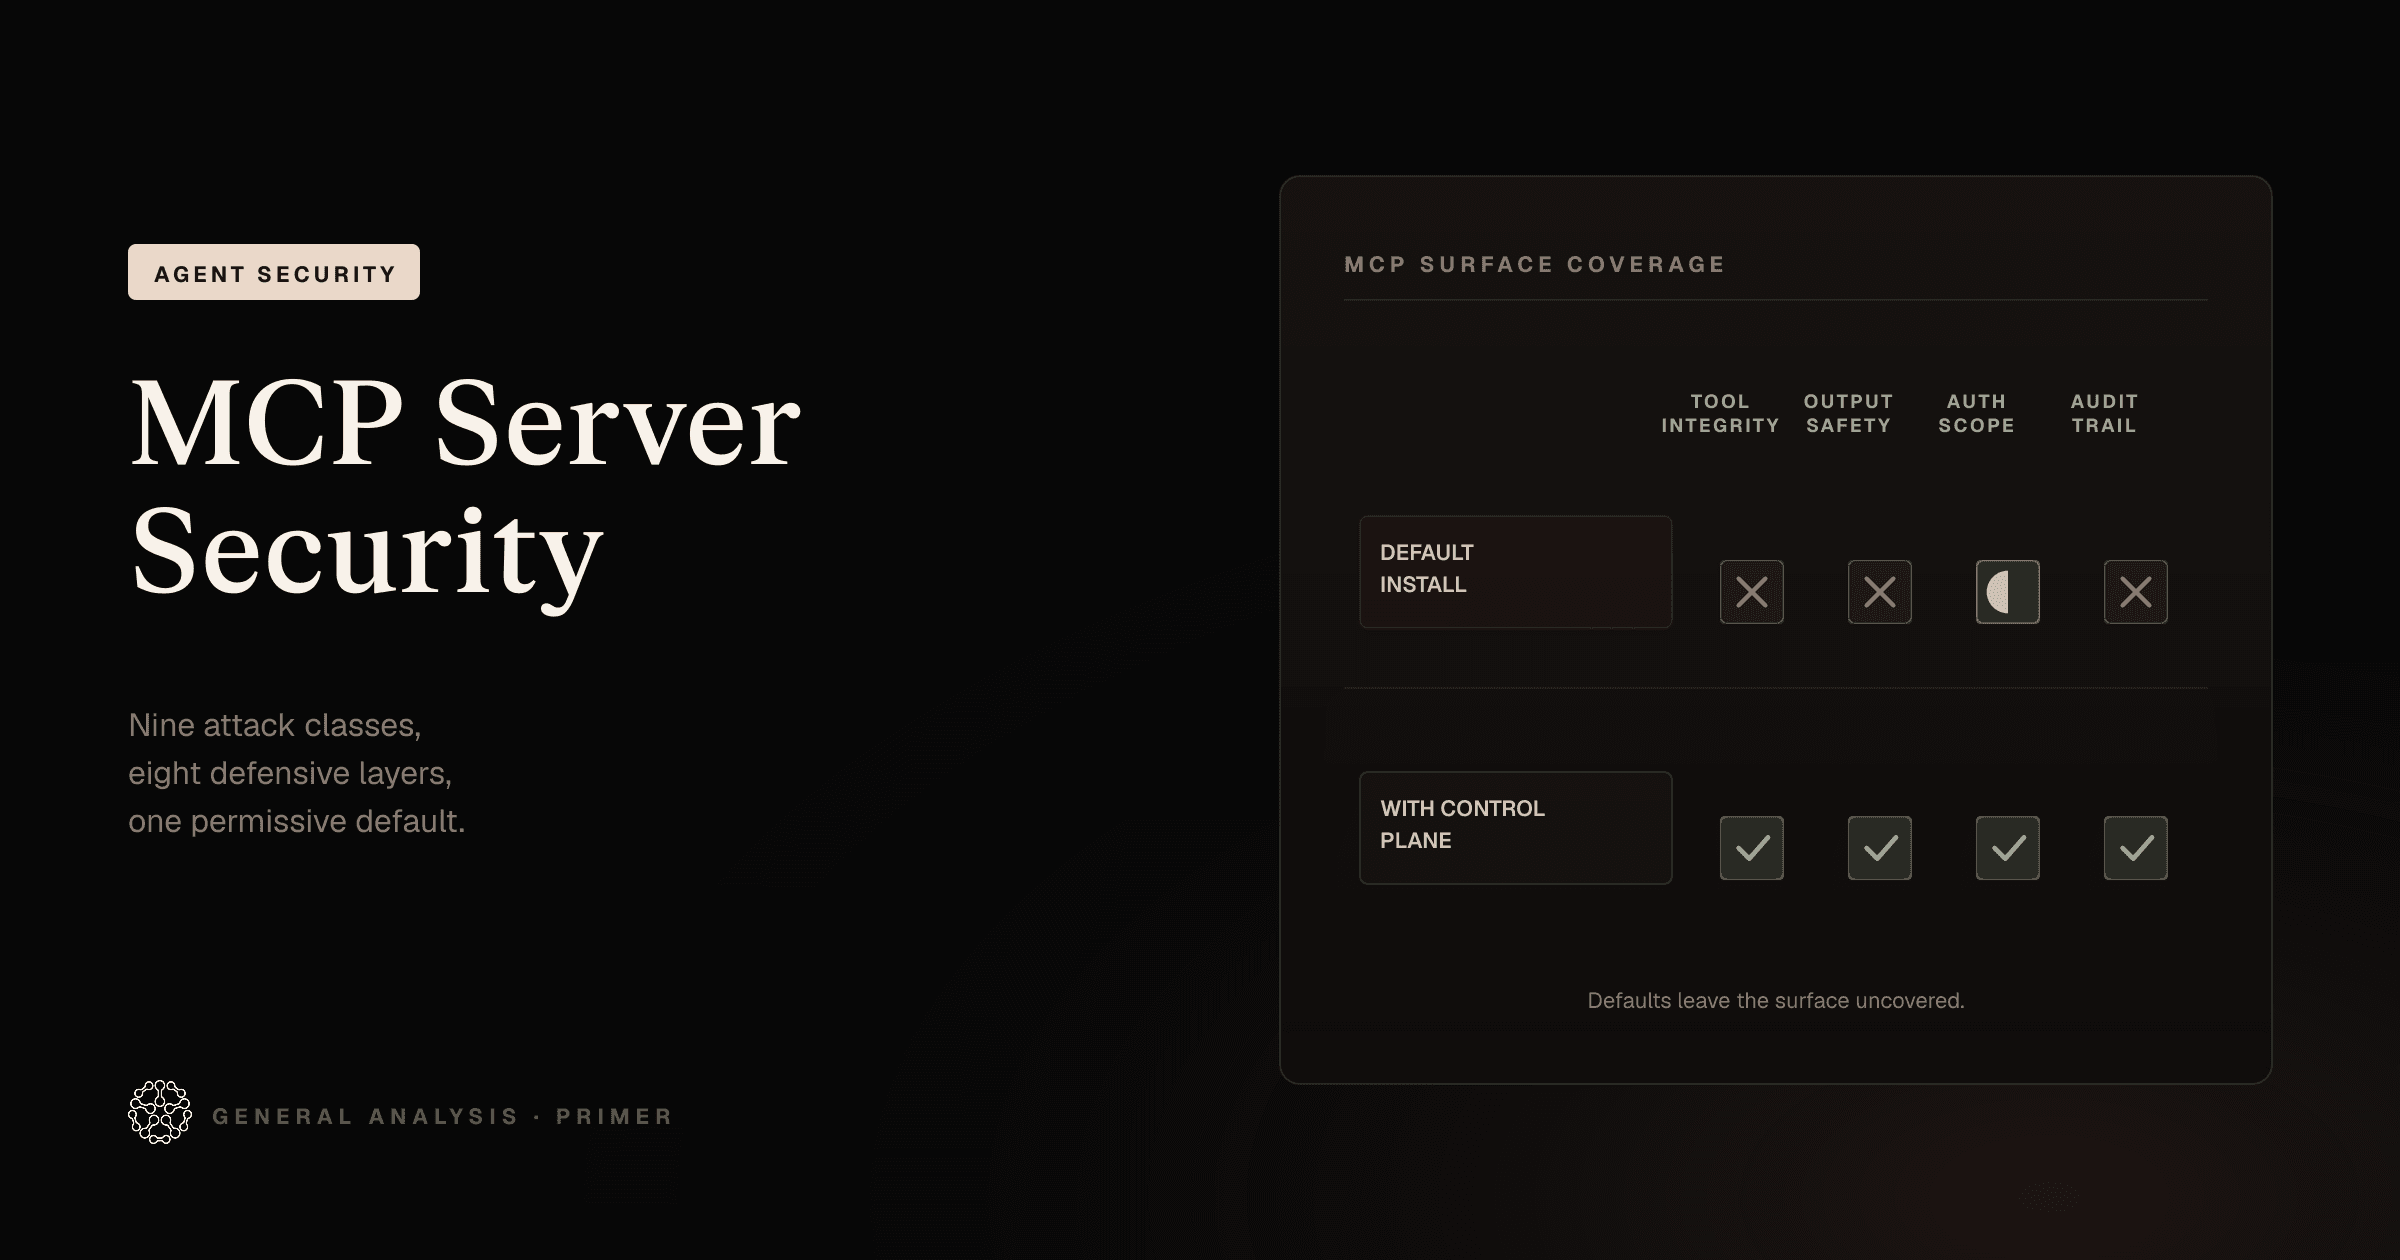
MCP Server Security: A Threat Model for Agent Tool Supply Chains
MCP servers put executable code, tool schemas, credentials, and agent context in one path. This primary-source threat model covers nine attack classes, current CVEs, and the controls that contain them.
May 2, 2026 · 16 min read
May 2, 202616 min read
 Guide·FRAMEWORK
Claude Cowork vs Claude Code: Security Differences for Enterprise
Claude Cowork and Claude Code share an agentic architecture but ship very different enterprise controls. A primary-source comparison of sandbox, network, audit-log, MCP, and decision-framework differences for security teams.
May 1, 2026 · 10 min read
May 1, 202610 min read
 Guide·PLAYBOOK
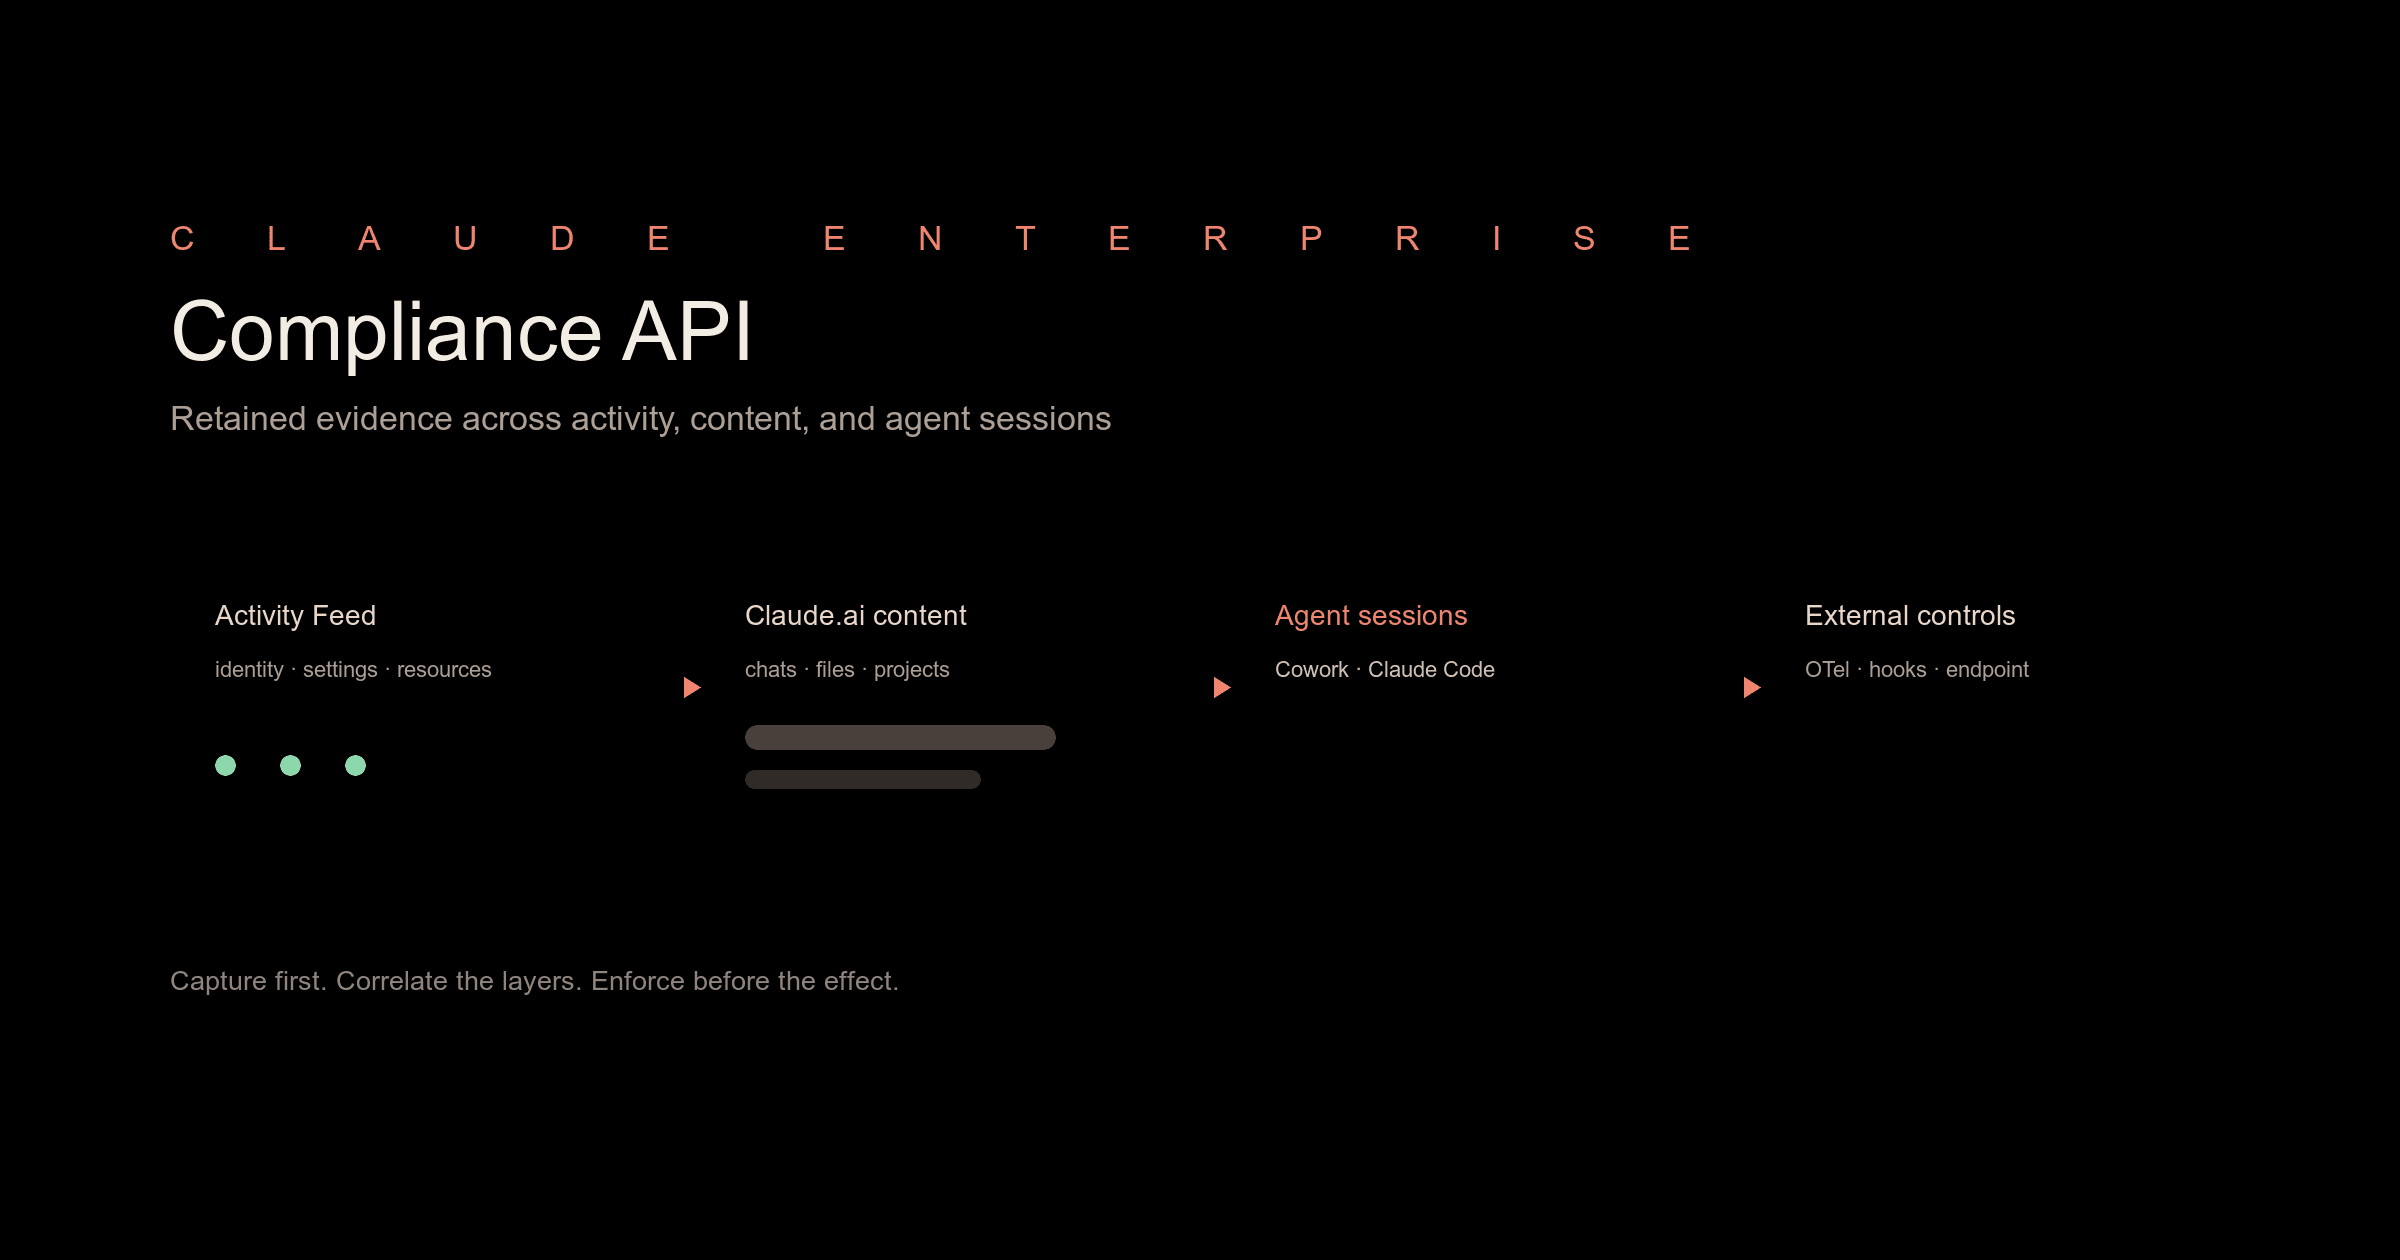
How to Audit Claude with the Compliance API
Anthropic's Compliance API exposes activity events, Claude.ai content, organization settings, and supported Cowork and Claude Code session transcripts. This guide explains current coverage, setup, retention, exclusions, and the controls that still need a separate enforcement layer.
May 1, 2026 · 13 min read
May 1, 202613 min read
 Guide·PLAYBOOK
How to Secure Claude Cowork
Claude Cowork brings Claude Code-style agentic work to local files, browsers, apps, plugins, and scheduled tasks. Here is how to put a middleman proxy, browser controls, computer-use limits, and enterprise monitoring around it before using it on real work.
April 30, 2026 · 16 min read
April 30, 202616 min read
 Blog·NEWS
General Analysis raises $10M to build the security arsenal for the agentic era
Led by Altos Ventures, with 645 Ventures and Menlo Ventures participating, the round funds an empirical security platform pairing adversarial simulation with production defenses.
April 29, 2026 · 4 min read
April 29, 20264 min read
 Guide·PRIMER
What Is AI Red Teaming? A Practitioner's Guide
AI red teaming is adversarial testing of AI systems to find exploitable vulnerabilities before attackers do. Learn how it works, key techniques, real exploit examples, and how to implement it.
April 15, 2026 · 18 min read
April 15, 202618 min read
 Blog·RESEARCH
50+ customer service agents offer $10,000,000+ in fabricated benefits
Our autonomous red-team agent elicited unauthorized offers from 50 of 55 public support bots, revealing how repeated attempts and nondeterminism turn small policy gaps into material risk.
March 22, 2026 · 10 min read
March 22, 202610 min read
 Guide·PRIMER
What Are AI Guardrails?
A complete guide to AI guardrails: what they are, the eight main types, how they work architecturally, and how to evaluate them for production LLM and agentic deployments.
March 15, 2026 · 12 min read
March 15, 202612 min read
 Guide·FRAMEWORK
OWASP Top 10 for Agentic AI: What Matters Most?
An analytical guide to the OWASP Top 10 for Agentic Applications 2026: what the ten risks are, how they relate to each other, and what they imply for builders of agentic systems.
March 15, 2026 · 10 min read
March 15, 202610 min read
 Guide·PLAYBOOK
Best AI Guardrails in 2026: Tools, Architecture, and How to Choose
Compare AI guardrails by control type, deployment, and limitations. Learn how to measure false positives, latency, and policy coverage before choosing a tool.
March 15, 2026 · 7 min read
March 15, 20267 min read
 Blog·PRODUCT UPDATES
Guardrail Release
Open-source release of the GA Guard series, a family of safety classifiers that have been providing comprehensive protection for enterprise AI deployments for the past year.
October 1, 2025 · 7 min read
October 1, 20257 min read
 Blog·RESEARCH
Claude Jailbroken to Mint Unlimited Stripe Coupons
We reveal a powerful metadata-spoofing attack that exploits Claude's iMessage integration to mint unlimited Stripe coupons or invoke any MCP tool with arbitrary parameters, without alerting the user.
July 16, 2025 · 7 min read
July 16, 20257 min read
 Blog·RESEARCH
Supabase MCP can leak your entire SQL database
Indirect prompt injection through support-ticket data lets an MCP-enabled assistant cross trust boundaries and query private tables with Supabase’s privileged service role.
July 8, 2025 · 8 min read
July 8, 20258 min read
 Blog·RESEARCH
Exploiting Partial Compliance: The Redact-and-Recover Jailbreak
We present the Redact & Recover (RnR) Jailbreak, a novel attack that exploits partial compliance behaviors in frontier LLMs to bypass safety guardrails through a two-phase decomposition strategy.
July 7, 2025 · 8 min read
July 7, 20258 min read
 Blog·RESEARCH
Case Study: Light-Weight Policy Moderators for Indeed Job Postings
Our compact policy moderation models achieve human-level performance at <1% per-review cost, outperforming GPT-4o and o4‑mini on F1 while running faster and cheaper.
May 25, 2025 · 8 min read
May 25, 20258 min read
 Blog·RESEARCH
Comparative Adversarial Analysis of Llama 4 Models
A head-to-head robustness evaluation of Llama 4 (Maverick, Scout) versus GPT‑4.1, GPT‑4o, Sonnet 3.7, etc. using TAP‑R, Crescendo, and Redact‑and‑Recover across HarmBench and AdvBench.
May 10, 2025 · 10 min read
May 10, 202510 min read
 Blog·NEWS
General Analysis x Together AI
The collaboration applies General Analysis red-teaming methods across Together AI’s model ecosystem and releases supporting tools, benchmarks, and an interactive TAP notebook.
May 6, 2025 · 2 min read
May 6, 20252 min read
 Blog·RESEARCH
The Jailbreak Cookbook
A field guide to manual and automated LLM jailbreaks, with a practical taxonomy, runnable implementations, and cross-model benchmarks for influential attack methods.
March 21, 2025 · 40 min read
March 21, 202540 min read
 Blog·RESEARCH
Generating Diverse Test Cases with Diversity Transfer from LegalBench
Seeding generation with LegalBench produced a broader set of realistic adversarial legal questions than zero-shot prompting, offering a practical way to improve benchmark coverage.
February 19, 2025 · 5 min read
February 19, 20255 min read
 Blog·RESEARCH
Red Teaming GPT-4o: Uncovering Hallucinations in Legal AI Models
In this work we explore automated red teaming, applied to GPT-4o in the legal domain. Using a Llama3 8B model as an attacker, we generate more than 50,000 adversarial questions that cause GPT-4o to hallucinate responses in over 35% of cases.
January 23, 2025 · 5 min read
January 23, 20255 min read